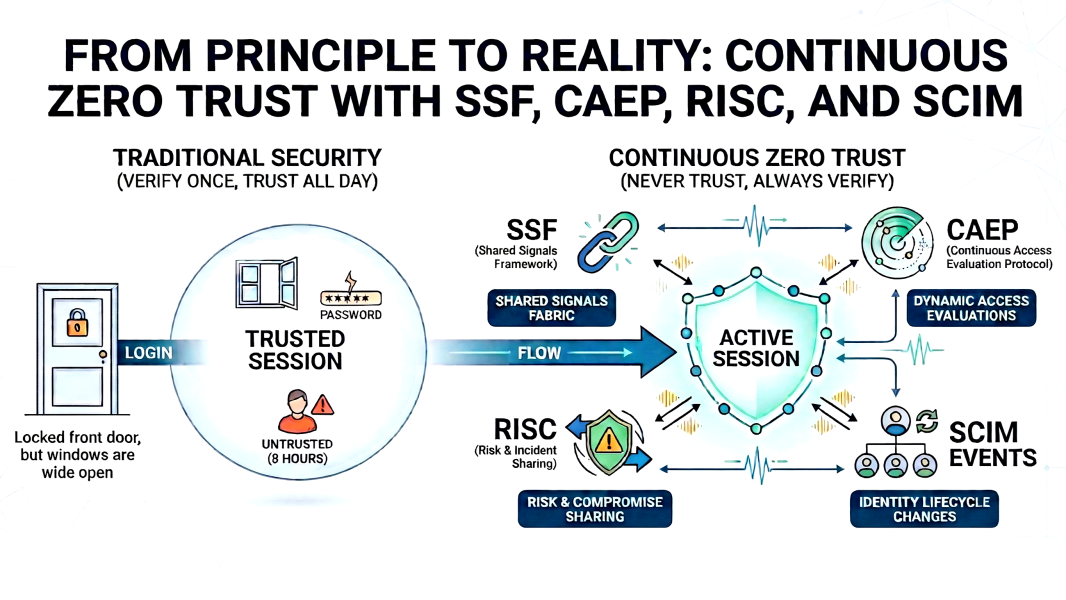
SSF, CAEP, RISC, and SCIM Events: Zero Trust signaling standards

SSF, CAEP, RISC, and SCIM Events: the standards turning Zero Trust from a principle into a reality

A practical breakdown of how SSF, CAEP, RISC, and SCIM Events work together to close the gap between Zero Trust as a principle and Zero Trust as a functioning architecture.

Continuous AccessMarch 5, 2026 · 6 min · 1172 words · Prithvi Poreddy

CAEP and Zero Trust: Why AI Agents Make This Critical (Part 4 of 4)

The future isn’t incremental. AI agents require transaction-level authorization. Zero Trust demands continuous verification. CAEP provides the infrastructure for both—and what’s coming in the next 3-5 years.

CAEP Explained · Part 4/4October 28, 2025 · 8 min · 1497 words · Prithvi Poreddy

Implementing CAEP: Architecture Patterns and Policy Design (Part 3 of 4)

From direct IdP connections to centralized event hubs—understand the architecture patterns that work at scale, how to design effective policies, and avoid common implementation pitfalls.

CAEP Explained · Part 3/4October 28, 2025 · 7 min · 1328 words · Prithvi Poreddy

How CAEP Events Actually Work: Real Scenarios You Face Today (Part 2 of 4)

From contractor termination to session revocation in under 3 minutes. See exactly how CAEP events flow through your systems and why different applications respond differently to the same security event.

CAEP Explained · Part 2/4October 27, 2025 · 9 min · 1762 words · Prithvi Poreddy

CAEP Explained: Why Your Federated Sessions Are Broken (Part 1 of 4)

A contractor’s access ends at 5 PM, but their sessions stay active for hours. This isn’t a bug—it’s how federation works. CAEP fixes the structural problem nobody talks about.

CAEP Explained · Part 1/4October 27, 2025 · 10 min · 2087 words · Prithvi Poreddy