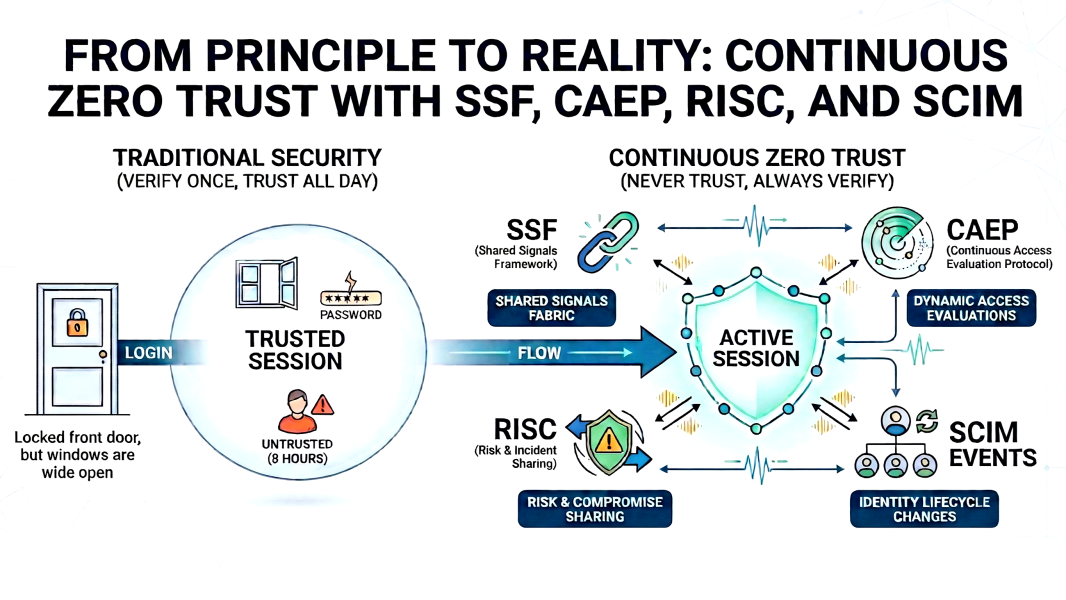
SSF, CAEP, RISC, and SCIM Events: Zero Trust signaling standards

SSF, CAEP, RISC, and SCIM Events: the standards turning Zero Trust from a principle into a reality

A practical breakdown of how SSF, CAEP, RISC, and SCIM Events work together to close the gap between Zero Trust as a principle and Zero Trust as a functioning architecture.

Continuous AccessMarch 5, 2026 · 6 min · 1172 words · Prithvi Poreddy

Build vs Buy for Identity Security: Strategy, Capability, and Risk

Stop asking if you can build. Start asking if you should. A framework to help identity and security teams make better build vs buy decisions by evaluating strategic necessity, execution capability, and total risk.

IAM ArchitectureJanuary 5, 2026 · 10 min · 2021 words · Prithvi Poreddy

CAEP Explained: Why Your Federated Sessions Are Broken (Part 1 of 4)

A contractor’s access ends at 5 PM, but their sessions stay active for hours. This isn’t a bug—it’s how federation works. CAEP fixes the structural problem nobody talks about.

CAEP Explained · Part 1/4October 27, 2025 · 10 min · 2087 words · Prithvi Poreddy

Making Sense of Identity's Alphabet Soup: ISPM, IVIP, and ITDR

A comprehensive guide to understanding how ISPM, IVIP, and ITDR work together to provide posture, visibility, and response for complete identity defense.

IAM ArchitectureOctober 8, 2025 · 8 min · 1588 words · Prithvi Poreddy

Identity Security Moves at the Speed of App Onboarding

The SCIM Acceleration Gateway helps IAM teams onboard apps in days instead of weeks by abstracting messy APIs behind a clean SCIM 2.0 facade.

Identity GovernanceSeptember 4, 2025 · 4 min · 738 words · Prithvi Poreddy

🌍 Global AI Governance: What It Means for Identity Security

Explores the implications of AI governance laws on identity security, emphasizing non-human identities and auditability.

AI AgentsAugust 27, 2025 · 3 min · 559 words · Prithvi Poreddy